Are your cyber investments actually moving the dial?
A consultant-led cyber risk program: 19 assessment activities, run on a recurring cadence by one team, quantified in financial terms — with the tooling included.
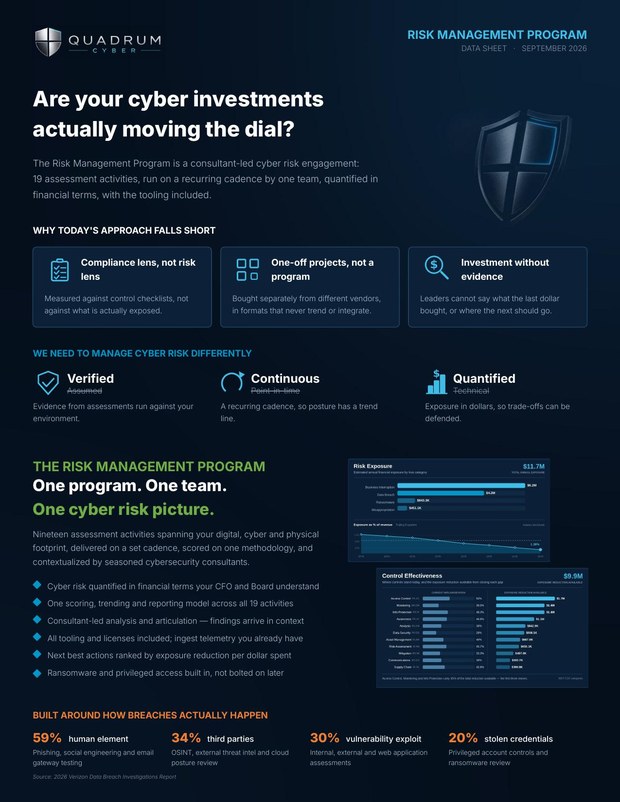
One Program. One Team. One Cyber Risk Picture.
Three tiers. One methodology. Meets you where you are.
Start at Core and grow into Plus and Enterprise as your organization’s needs and capabilities mature. The methodology, scoring and reporting stay identical across tiers, so you maintain risk trending context.
- Remote delivery, consultant in the middle
- Cyber risk quantification built in
- Controls effectiveness measurement, not just compliance
- Remote and on-site delivery
- Adds backup, privileged access, wireless, physical, social vectors: SMS, QR, Deepfake
- 1 internal + 1 external verification scan each quarter
- Remote and on-site delivery
- Adds board insights, ransomware and cloud review
- 2 internal + 2 external verification scans each quarter
Nineteen activities in the program, plus evolving optional modules.
Risk Management Program activities span the digital, cyber and physical footprint. Select any activity to read what it covers.
| Program activity | CORE | PLUS | ENTERPRISE | Activity frequency |
|---|
Risk you can see, price and defend.
Findings are contextualized and prioritized so you can make risk-informed decisions when they matter.
Three reports, one data set.
What the program delivers on every cycle.
Assessment Report
Issued for each assessment activity. Every finding carries its severity, a summary of the risk, the potential business impact, and the specific remediation steps to close it.
One-Pager Summary
Front of every Assessment Report: the result analysed on a single page and set against industry peers, so the conclusion survives the walk to the boardroom.
Quarterly Executive Risk Summary
Everything performed that quarter in one place — risk metrics with KPIs and KRIs, quarter-over-quarter trends, and a prioritized list of risk-reduction recommendations.
Same evidence. Four audiences.
Reporting is never re-run or re-scored for a given audience — it is the same measurement, contextualized for the decision each reader actually makes.
Board of Directors
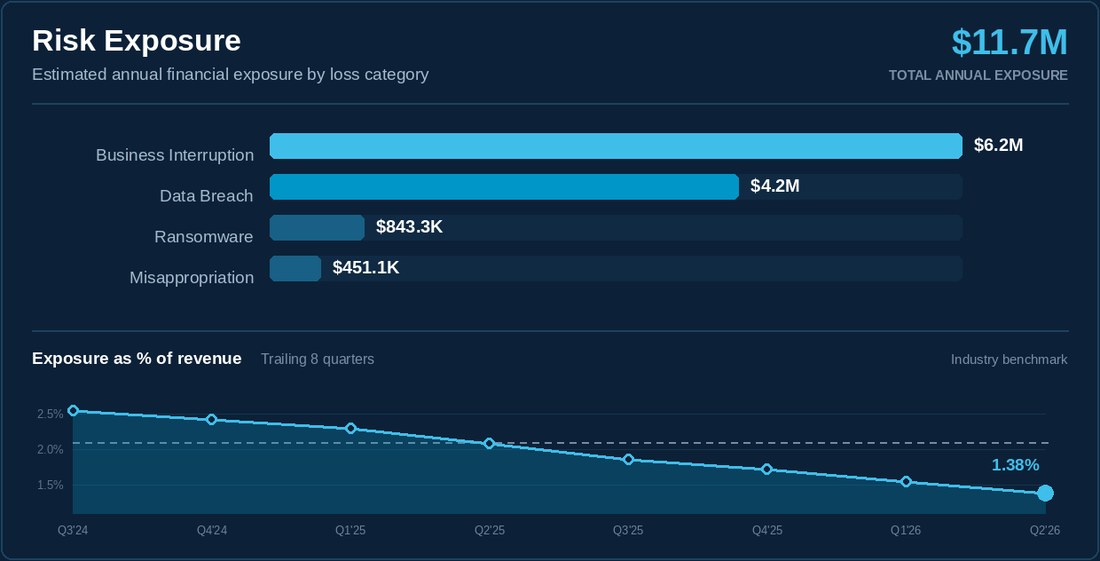
Exposure in dollars, the trend line, and whether oversight duties are being met.
Executives
What the last dollar bought, what the next one should, and the operational risk behind it.
CISO
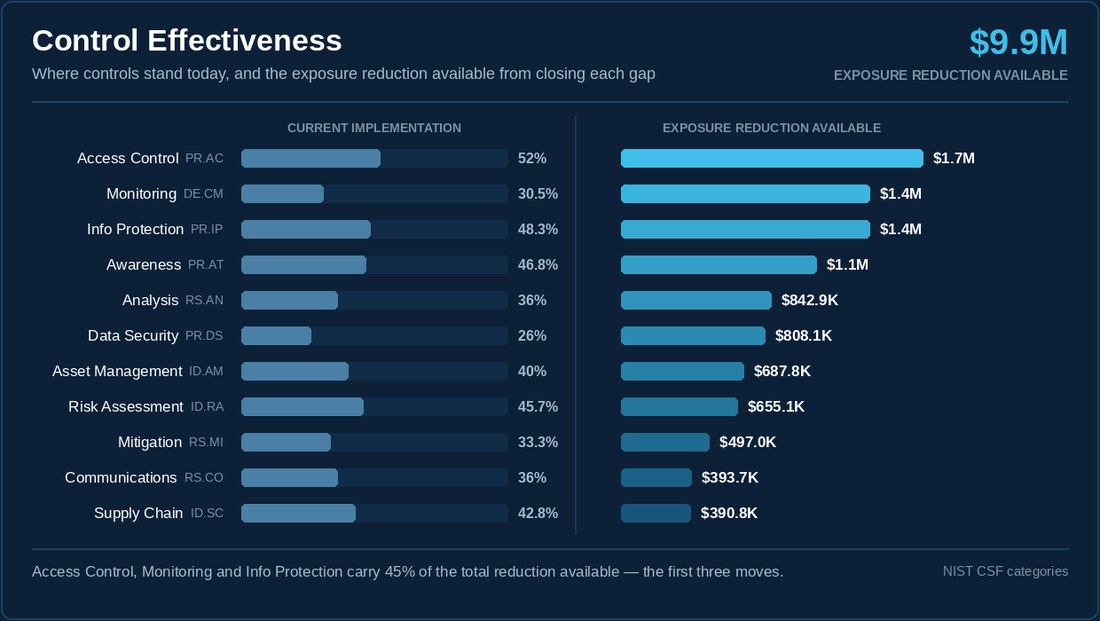
Control effectiveness across the domain areas, ranked by exposure removed per dollar.
Security Practitioners
The findings themselves — severity, evidence, affected assets and the fix.
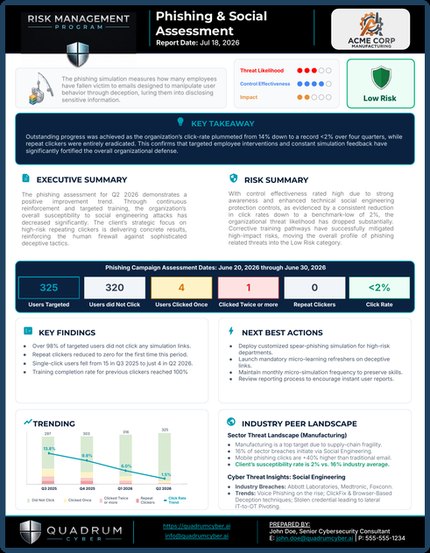
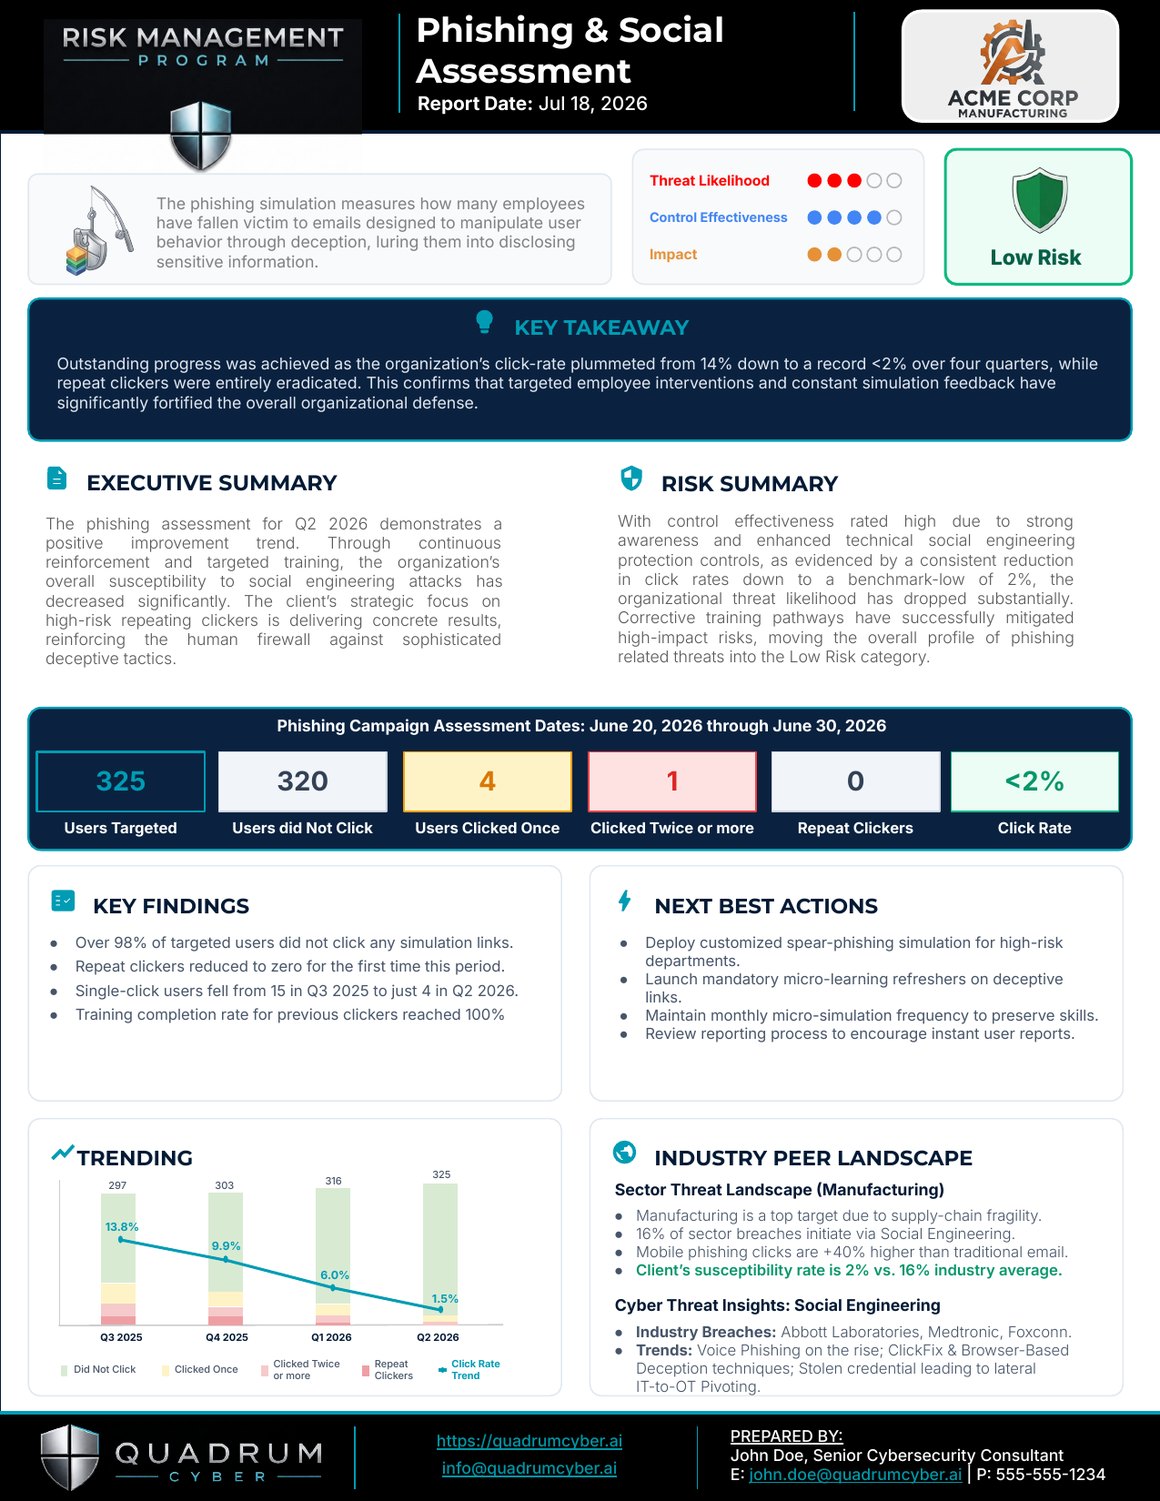
The Phishing & Social Engineering Assessment, as the executive sees it.
Executive summary · risk rating · control effectiveness · key findings · next best actions · industry peer landscape · quarter-over-quarter trending — all from the same measurement the practitioner is working from, written for the person who has to make the call.
Select the report to view it full size.
Built for the CISO who has to answer for the spend.
Why this is not another assessment.
Proven CRQ methodology
Risk quantification grounded in nearly two decades of actuarial data — built in and enabled from the Core tier, not sold as a premium module.
One program, not five vendors
Consistent reporting, scoring and trending across every activity. Nobody is left stitching five vendors' PDFs into a board narrative.
Consultants, not just a console
Seasoned practitioners run the assessments and interpret them. The platform carries the evidence; the advisor carries the argument.
Evolves with the threat
Ransomware susceptibility and privileged account controls are program activities — because that is where the breaches are.
Earned for managing cyber risk the right way.
QuadRMP Certification is awarded exclusively to Risk Management Program clients who have met and maintained every requirement of the program, and who have been brought before a Certification Board of globally recognized cybersecurity experts and leaders. It is not a questionnaire, a self-attestation or a logo that comes with the contract.
Meet every requirement
Full delivery of the activities in your tier, with findings remediated to the agreed thresholds — not merely reported and carried forward.
Hold it across cycles
Certification reads a trend line, not a moment. Performance has to be sustained across consecutive delivery cycles, and it is re-tested every year.
Defend it before the Board
Posture and evidence are presented to a Certification Board of globally recognized cybersecurity experts and leaders, who decide. Quadrum does not award it alone.
- Board and audit committee assurance, backed by evidence rather than intent
- Cyber insurance placement and renewal conversations
- Customer, partner and supply-chain due diligence
- Demonstrating a managed, measured program to regulators
Certification is held for as long as program requirements continue to be met, and is withdrawn if they are not.
See your own risk picture.
We will walk your environment through the program model and show you what the first cycle would measure.